the wire · #gadgets · 2026-10-01
This fake Mac Zoom installer has a sneaky way to bypass Gatekeeper
Cech Tech Reviews
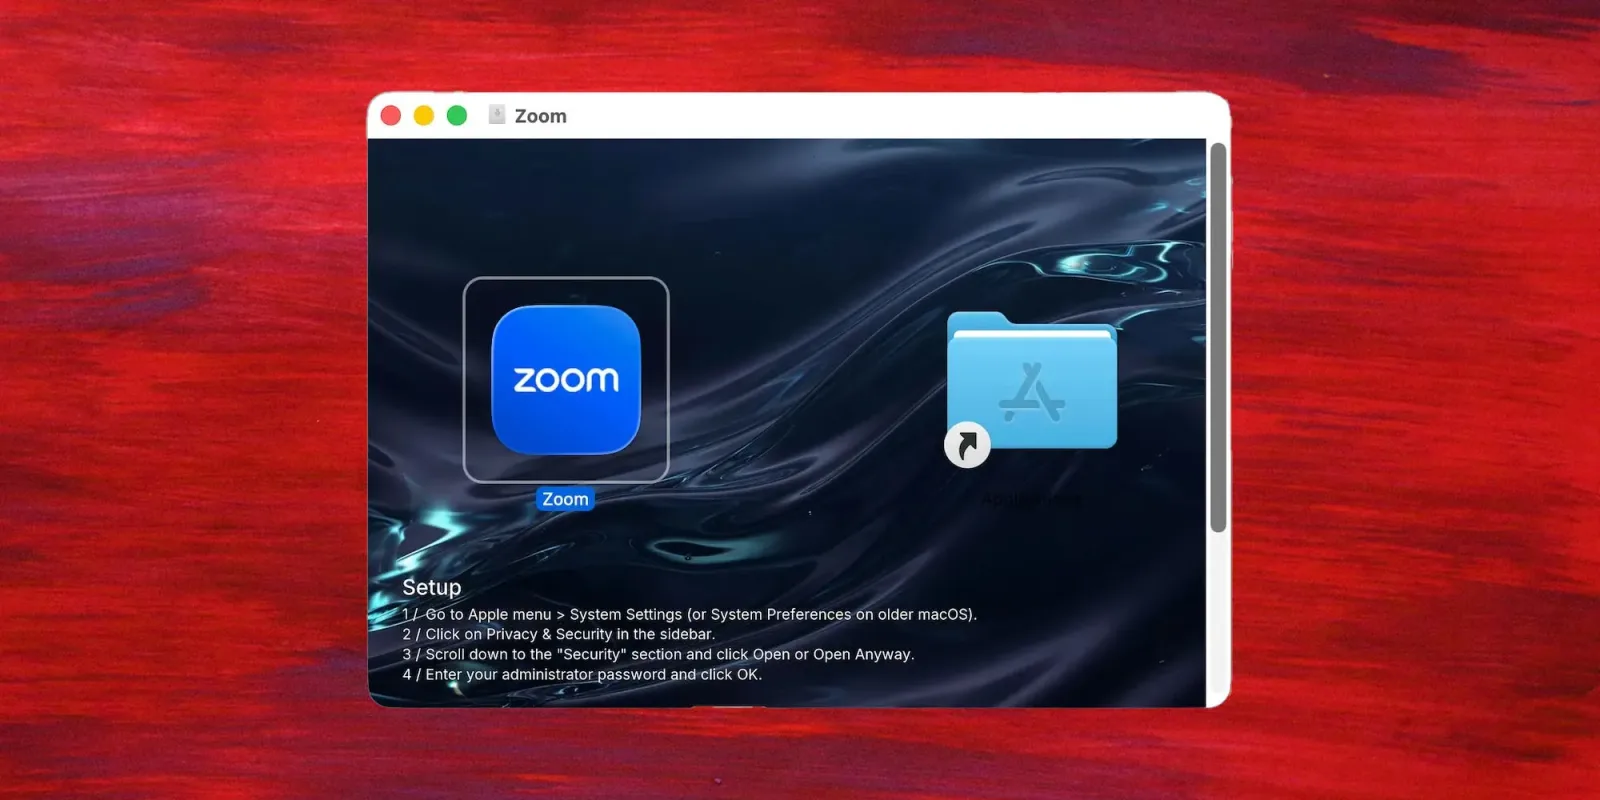
Cybersecurity researchers at Jamf found a Mac malware campaign that's smarter than most. According to their report, attackers are distributing a fake Zoom installer that sidesteps Apple's Gatekeeper security layer while still giving users what they expect: a working copy of Zoom.
The trick is in the execution. Most fake installers get flagged because they only deliver malware. This one installs the legitimate Zoom app and an infostealer in parallel, so the user sees Zoom launch and assumes everything is fine. Meanwhile, the malware is harvesting data and sending it to an attacker-controlled server in the background.
This approach is particularly dangerous because it exploits user trust at the moment of least suspicion. You downloaded something, it works as expected, so your guard drops. The malware gets a foothold while you're joining your first meeting.
Gatekeeper is designed to block unverified software, but attackers are finding ways around it by piggybacking on the installation flow of known apps. If the malware can mimic enough of a legitimate install process, it buys time before detection. Apple will likely patch the specific bypass method Jamf identified, but the broader tactic, bundling real software with hidden payloads, is worth watching.
The rise of AI-assisted social engineering makes this threat more scalable. Attackers can now use LLMs to craft convincing phishing emails, fake download pages, and support chats that direct users to malicious installers. The technical sophistication of the malware matters less when the initial compromise happens through a polished, AI-generated lure.
What this means for you: download apps only from official sources, the Mac App Store or the vendor's verified website. If you're managing a team, consider using an AI assistant to draft a security policy reminder. Try this prompt: "Write a brief, friendly Slack message explaining why our team should only download work apps from official sources, and what to do if they accidentally installed something suspicious." That kind of proactive communication, multiplied across your org, is often the simplest defense against socially engineered attacks.
Reporting basis: original story
← back to The Wire